Cyber regulation readiness · UK energy and regulated sectors
You may be about to become a regulated organisation.
The Cyber Security and Resilience Bill brings managed service providers, load-control operators and much of the energy supply chain under cyber regulation for the first time. We help you work out what applies, and get ready before a regulator asks.
Advice and software, from the same team
Senior consulting, and the tooling we built doing it.
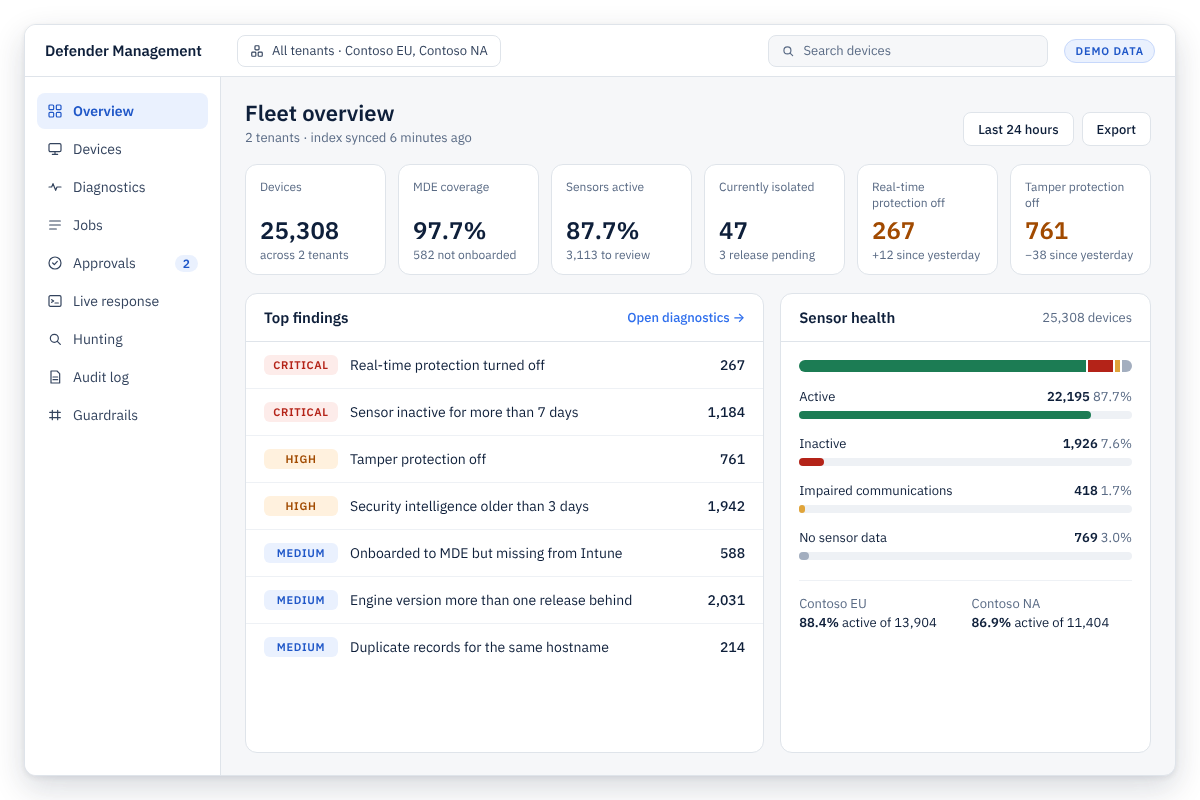 Explore Defender Management →
Product · Defender Management
Run Microsoft Defender like the estate you actually have.
For security engineering teams running tens of thousands of devices across several tenants, where one wrong click is an incident of its own.
- Defender for Endpoint, Intune and Entra ID in one correlated index
- Bulk actions with eligibility previews, protected tags and four-eyes approval
- Fleet live response, tracked jobs and a complete audit trail
Am I in scope?
The detail arrives later, in secondary legislation, but the direction of travel is clear enough to plan against. Any of these makes it worth a conversation now.
- You provide managed IT, cloud or security services to other businesses
- You hold an Ofgem licence: generation, supply, distribution or an IDNO
- You aggregate flexibility, or control load across customer sites
- You sell into utilities, and customers have started sending security questionnaires
- You are already a NIS operator in water, transport, health or digital infrastructure
- You report against the CAF and need to move to version 4.0
Two things happening alongside the Bill
DESNZ and Ofgem have consulted on baseline cyber requirements for all licensees, with enhanced obligations for the most significant operators.
Separately, the NCSC's move to CAF 4.0 means organisations comfortable with their last assessment are now measured against changed expectations.
Not sure? Ask on a free call →Services
Five services, all delivered at senior level. You work directly with the consultant who writes the report.
CAF readiness assessment
A gap assessment against the NCSC Cyber Assessment Framework, with findings prioritised by regulatory exposure and a costed remediation roadmap you can take to a board.
Fixed feeCompliance advisory
Scope determination, incident reporting readiness and evidence preparation for Ofgem, or whichever authority ends up regulating you.
Day rateVirtual CISO
Retained security leadership for direction, board reporting and the regulatory relationship, without a full-time hire.
Monthly retainerCyber Essentials
Guided implementation of the five controls, through to certification: what procurement teams across the energy supply chain ask for first.
Fixed feeMicrosoft Defender setup
Endpoint protection, email security and alerting configured properly across your Microsoft 365 estate. Running Defender at fleet scale? See Defender Management.
Fixed feeFees are quoted after the scoping call, once the scope is known. Ask for the rate card and you will get one.
How an engagement runs
Short, and deliberately easy to stop after any stage.
- Step 1
A call, at no cost
Thirty minutes to work out whether regulation reaches you, and whether there is anything worth paying for.
- Step 2
A fixed-fee assessment
An agreed scope, a fixed price and a defined end date, ending in a findings report and a roadmap.
- Step 3
Support, only if you want it
Run the roadmap yourselves, or keep us on retainer. The report is written to stand on its own.
About Ridgeway Security
Founded by Matthew James, whose career in cyber security has centred on the systems that keep Great Britain's critical national infrastructure running.
Working inside critical national infrastructure teaches you what a regulator actually reads, why a control that looks sensible on paper fails on a site with three people and one maintenance window a year, and how to tell a finding that matters from one that fills a report.
We take a small number of clients at a time: senior attention on every engagement, and occasionally a wait for a start date.
Worth saying plainly
- One consultant, start to finishThe person on the scoping call does the work.
- Fixed fees wherever possibleScope agreed up front, so the invoice is not a surprise.
- Independent adviceWe resell no third-party products and take no vendor commission. We build our own tooling, and only suggest it where it fits.
- Plain EnglishReports written for the board and the engineers, not the framework.
Talk to us
A free 30-minute scoping call about regulation, or a briefing on Defender Management against your own estate. No charge and no pitch.
Prefer email? enquiries@ridgewaysecurity.co.uk