Products / Defender Management
Defender Management
Operations at enterprise scale for Microsoft Defender.
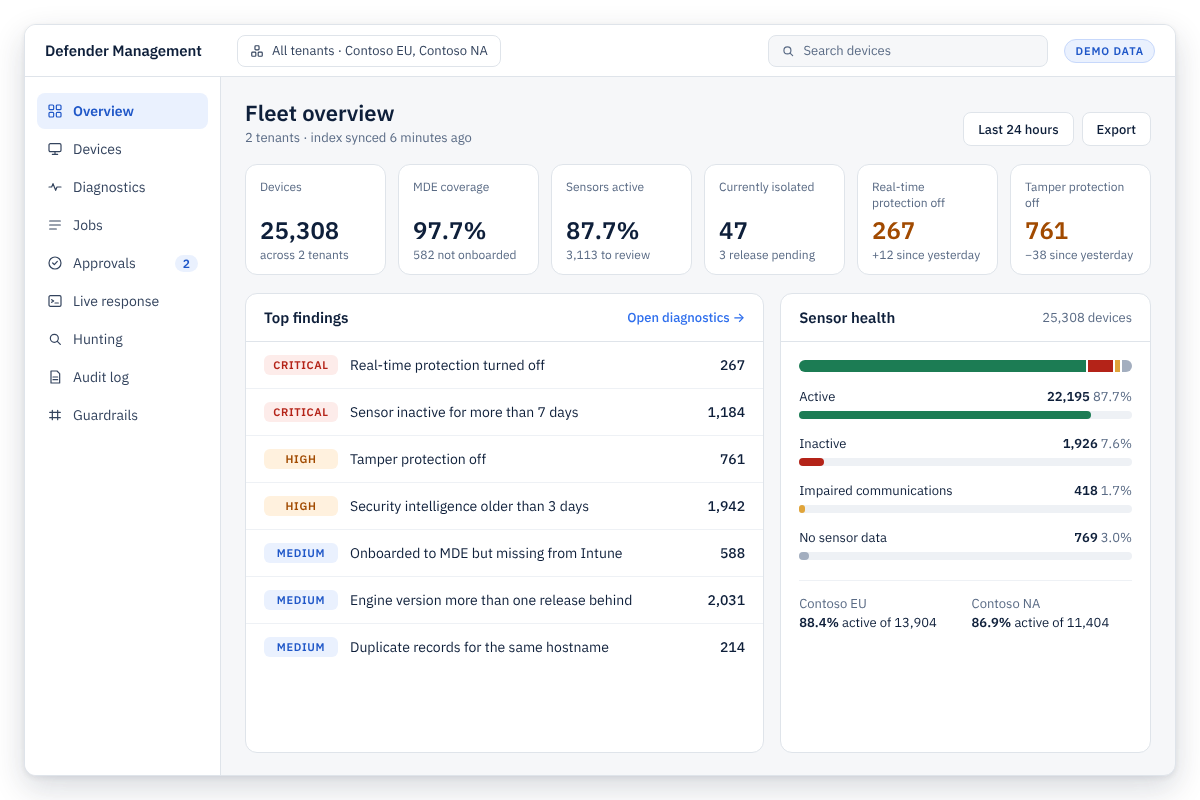
One correlated device index across Defender for Endpoint, Intune and Entra ID, with guarded bulk actions, fleet-wide live response, health diagnostics and a complete audit trail, for tens of thousands of devices across several tenants.
Overview
Defender Management in just over a minute
The problem
Where the portal runs out of road
At ten thousand devices and more, the gaps stop being inconvenient and start being risky.
Capabilities
What's in the product
Correlated device inventory
Defender for Endpoint, antivirus and Intune state per device, with saved views, facets and automatic detection of coverage gaps and duplicate records.
Guarded bulk actions
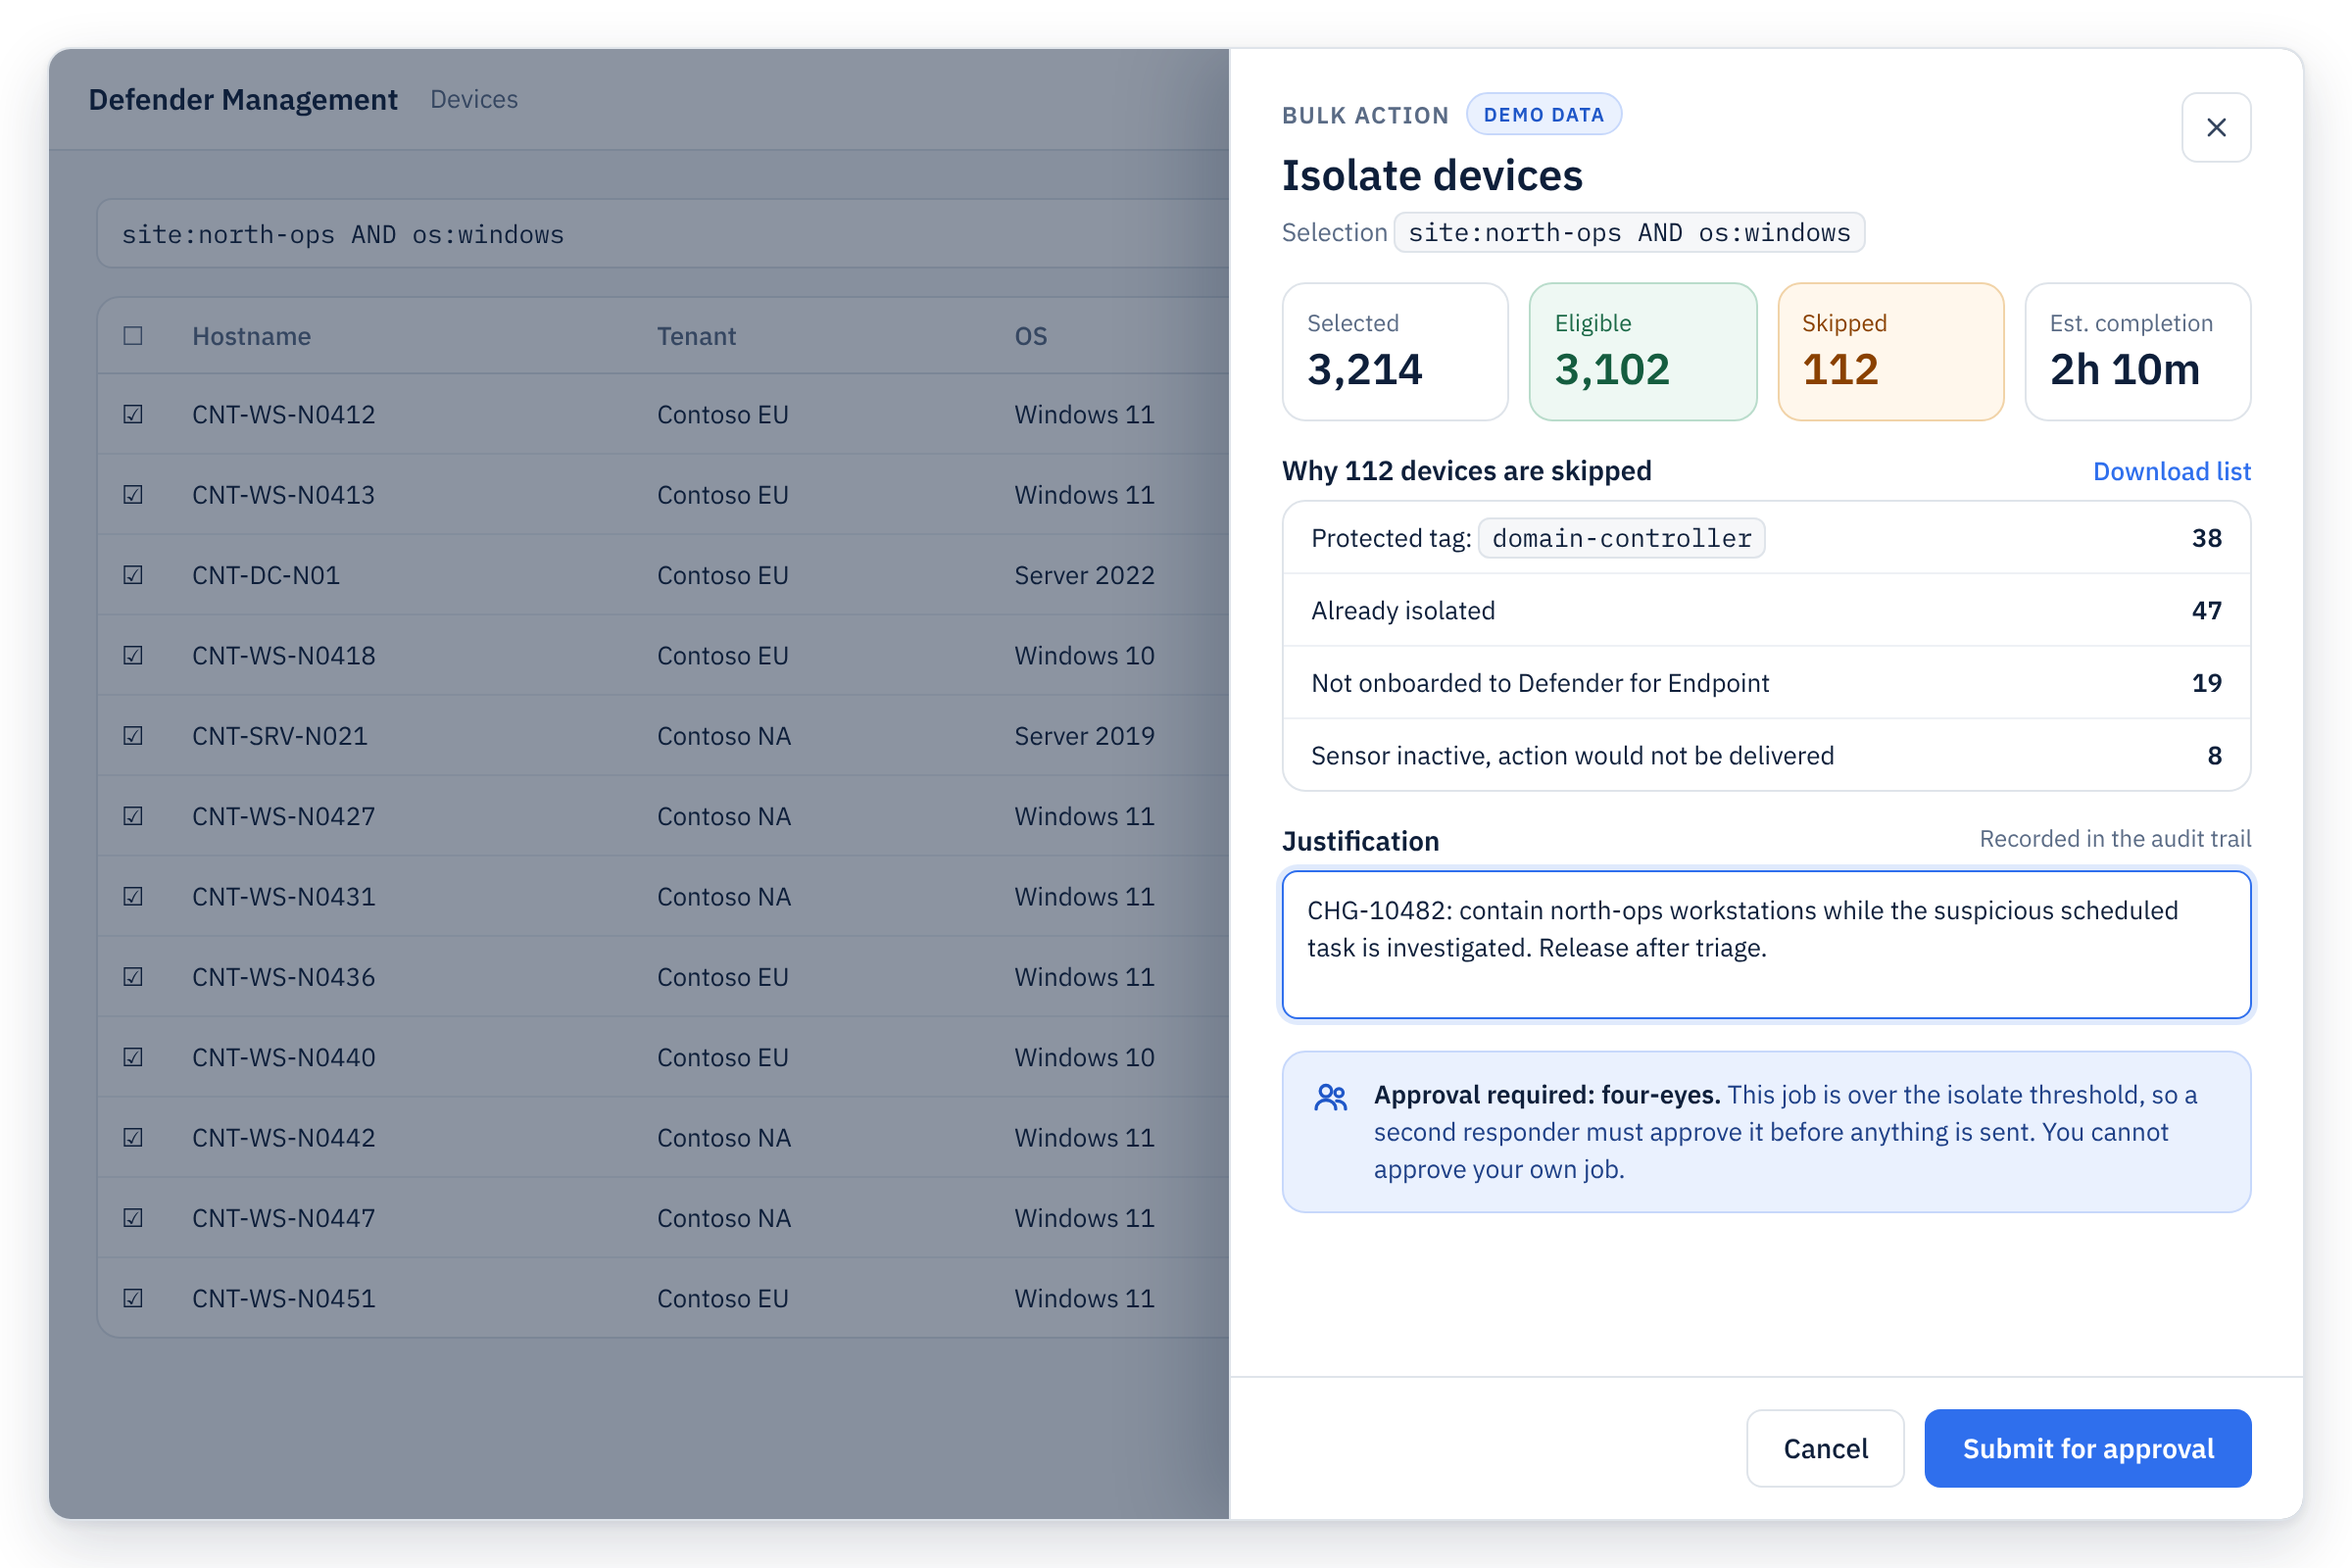
Isolate, release, restrict, scan, collect investigation packages, quarantine, offboard and tag, each with an eligibility preview: what runs, what is skipped and why, the ETA and whether approval is needed.
Fleet live response
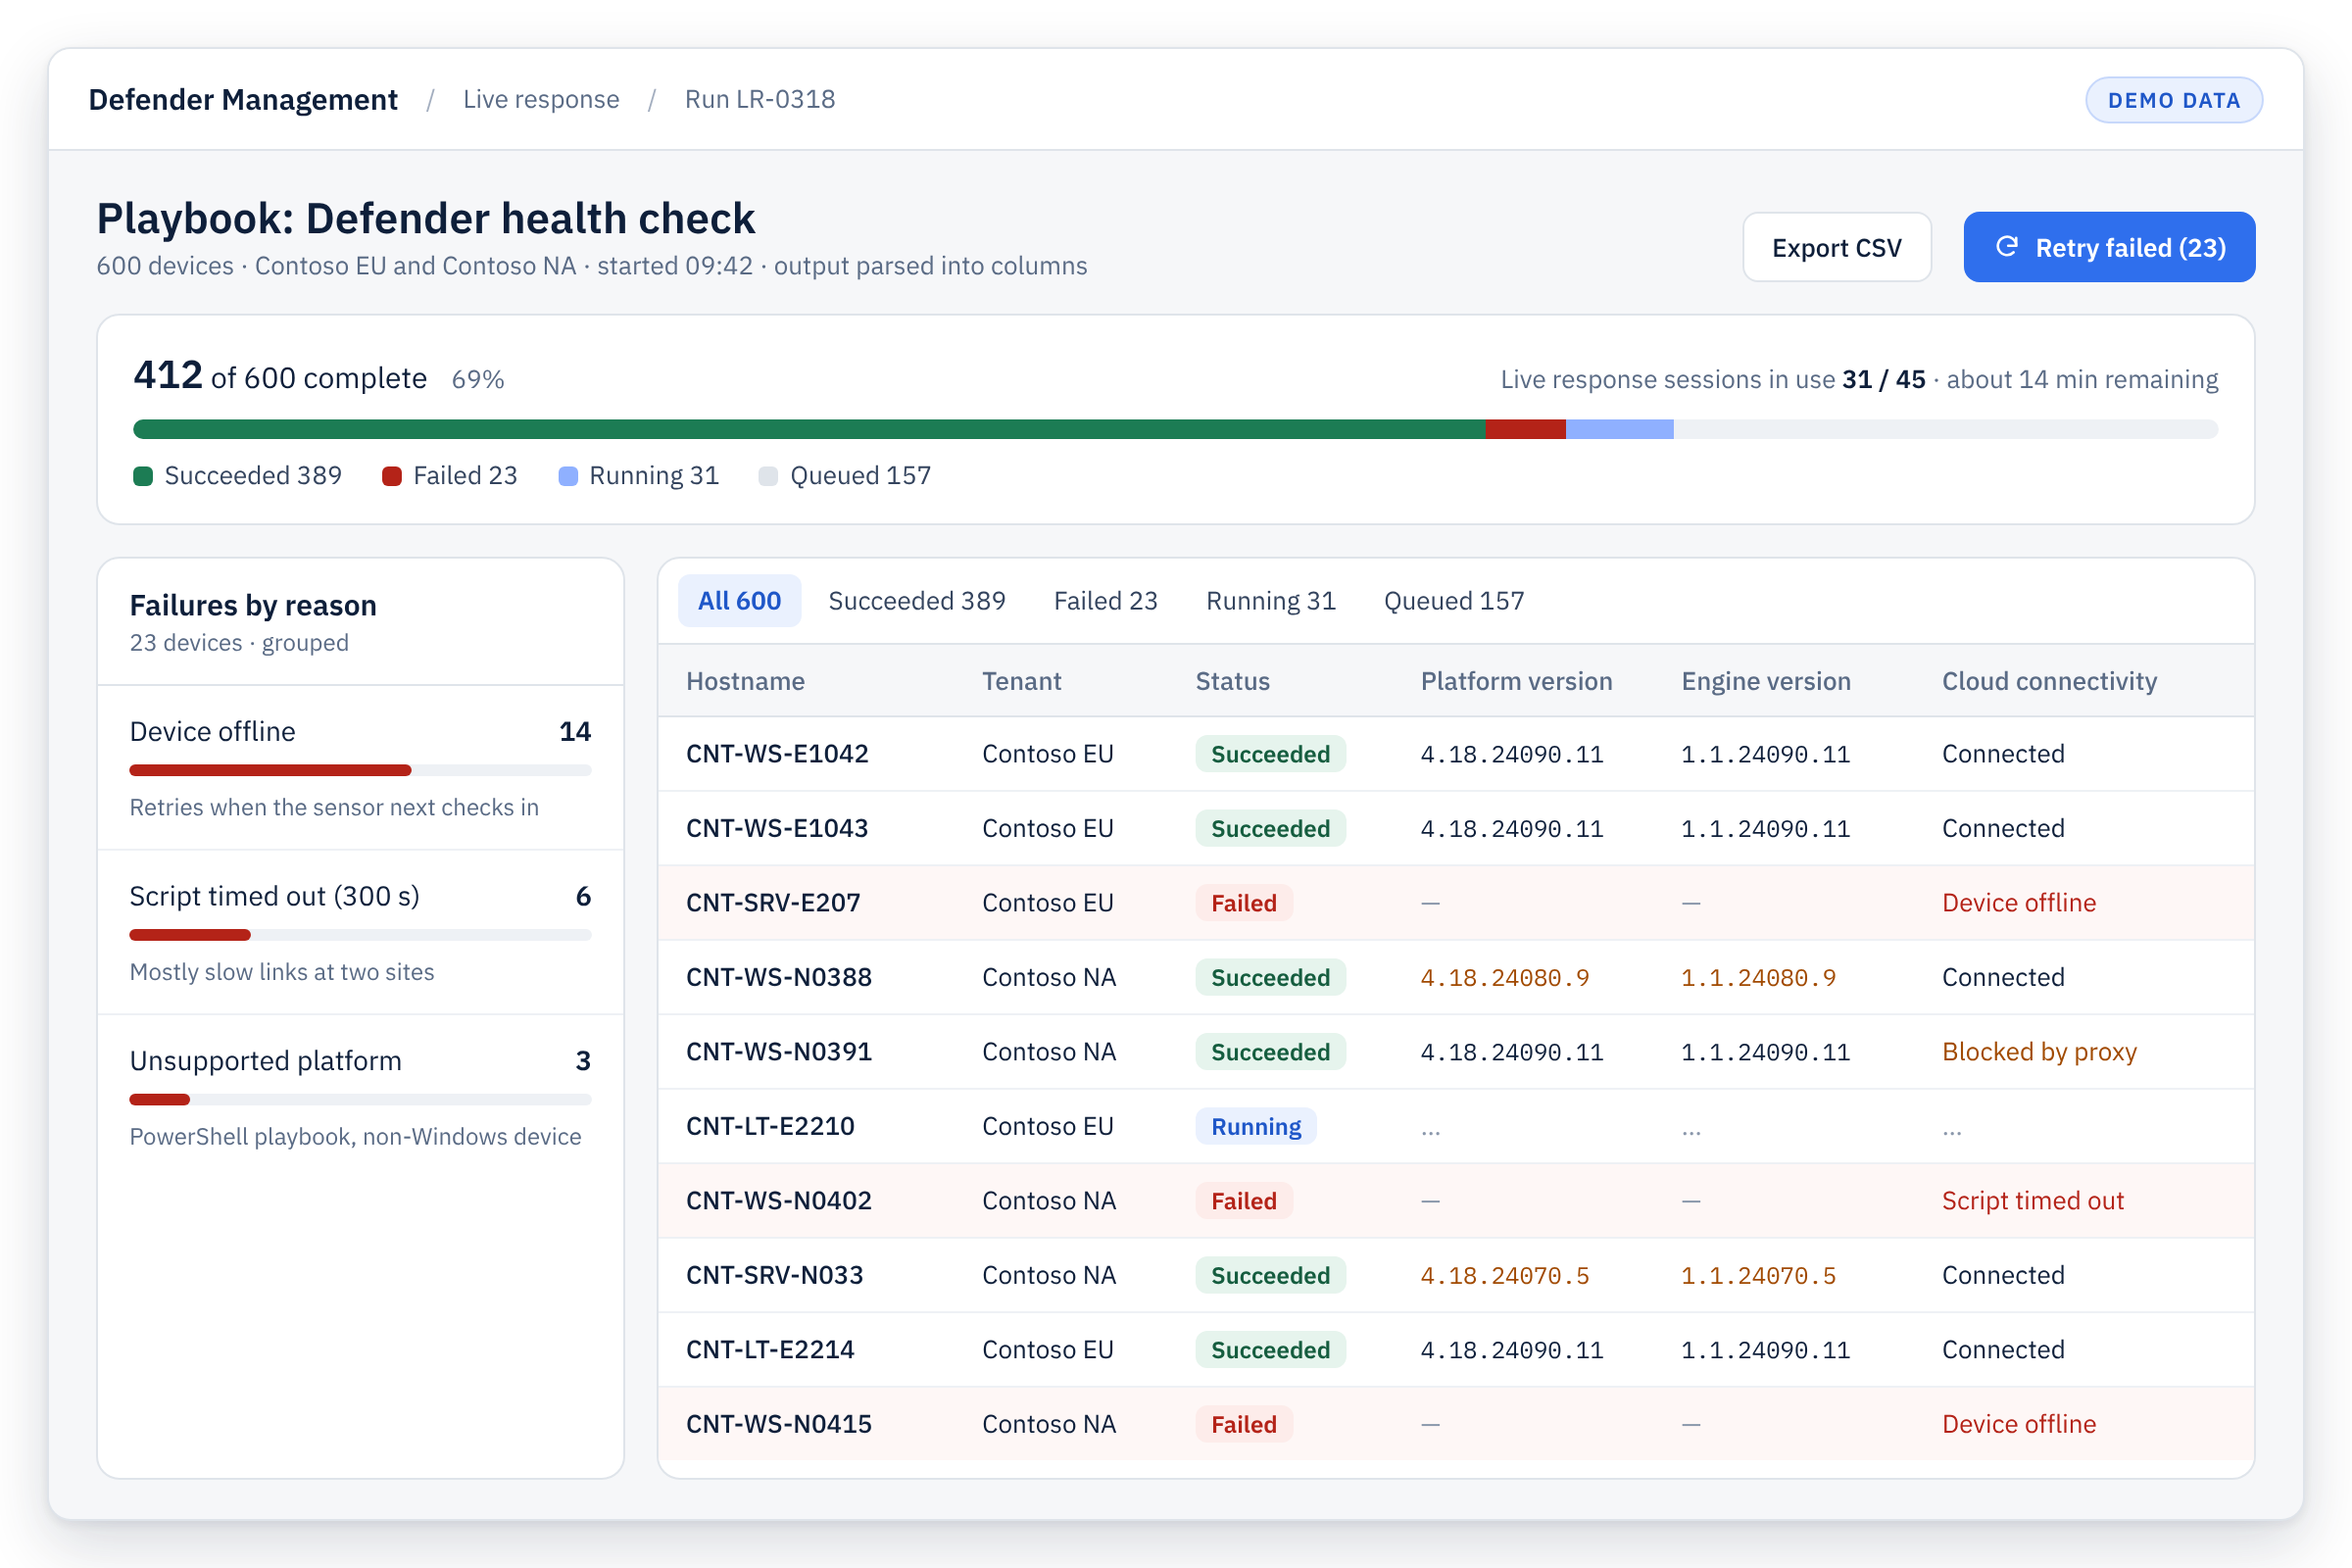
Built-in playbooks for Defender health, antivirus configuration, connectivity, event-log errors, repair, false-positive restore, platform rollback and Defender for Identity readiness. Write your own with run-time inputs.
Health diagnostics
14 built-in rules covering sensor, antivirus, coverage, containment and hygiene, plus custom rules in the same query language. Each explains why it matters and launches remediation against exactly the matching devices.
Automation
Scheduled jobs, tag rules that keep Defender tags in sync with any query, scheduled diagnostics digests, and Teams, Slack or signed-webhook notifications.
Change-ticket integration
ServiceNow and Jira create jobs through signed inbound webhooks, and get job status and failed devices written back to the ticket.
Indicators and hunting
Validated indicator import across tenants with expiry tracking and bulk extend or delete. One KQL query across every tenant, then act on the devices it returns.
Identity and incident signals
Defender for Identity sensor health and deployment status, one queue of open XDR incidents from every tenant, and Office 365, cloud-app and identity alerts in one place.
Multi-tenant by design
Every query, hunt, job and dashboard spans all connected tenants, for estates shaped by mergers, regions or subsidiaries.
How it works
From signal to audited action
- 01Defender for Endpoint, Intune and Entra ID
- 02Correlated device index
- 03Query, diagnose and act
- 04Guardrails and four-eyes approval
- 05Tracked jobs and audit trail
All screenshots show simulated demonstration data. No customer information is displayed.
Control
Governance built in
- Role-based access. Reader, operator, responder and admin roles.
- Four-eyes approval. Per-action thresholds, with a different, sufficiently privileged approver.
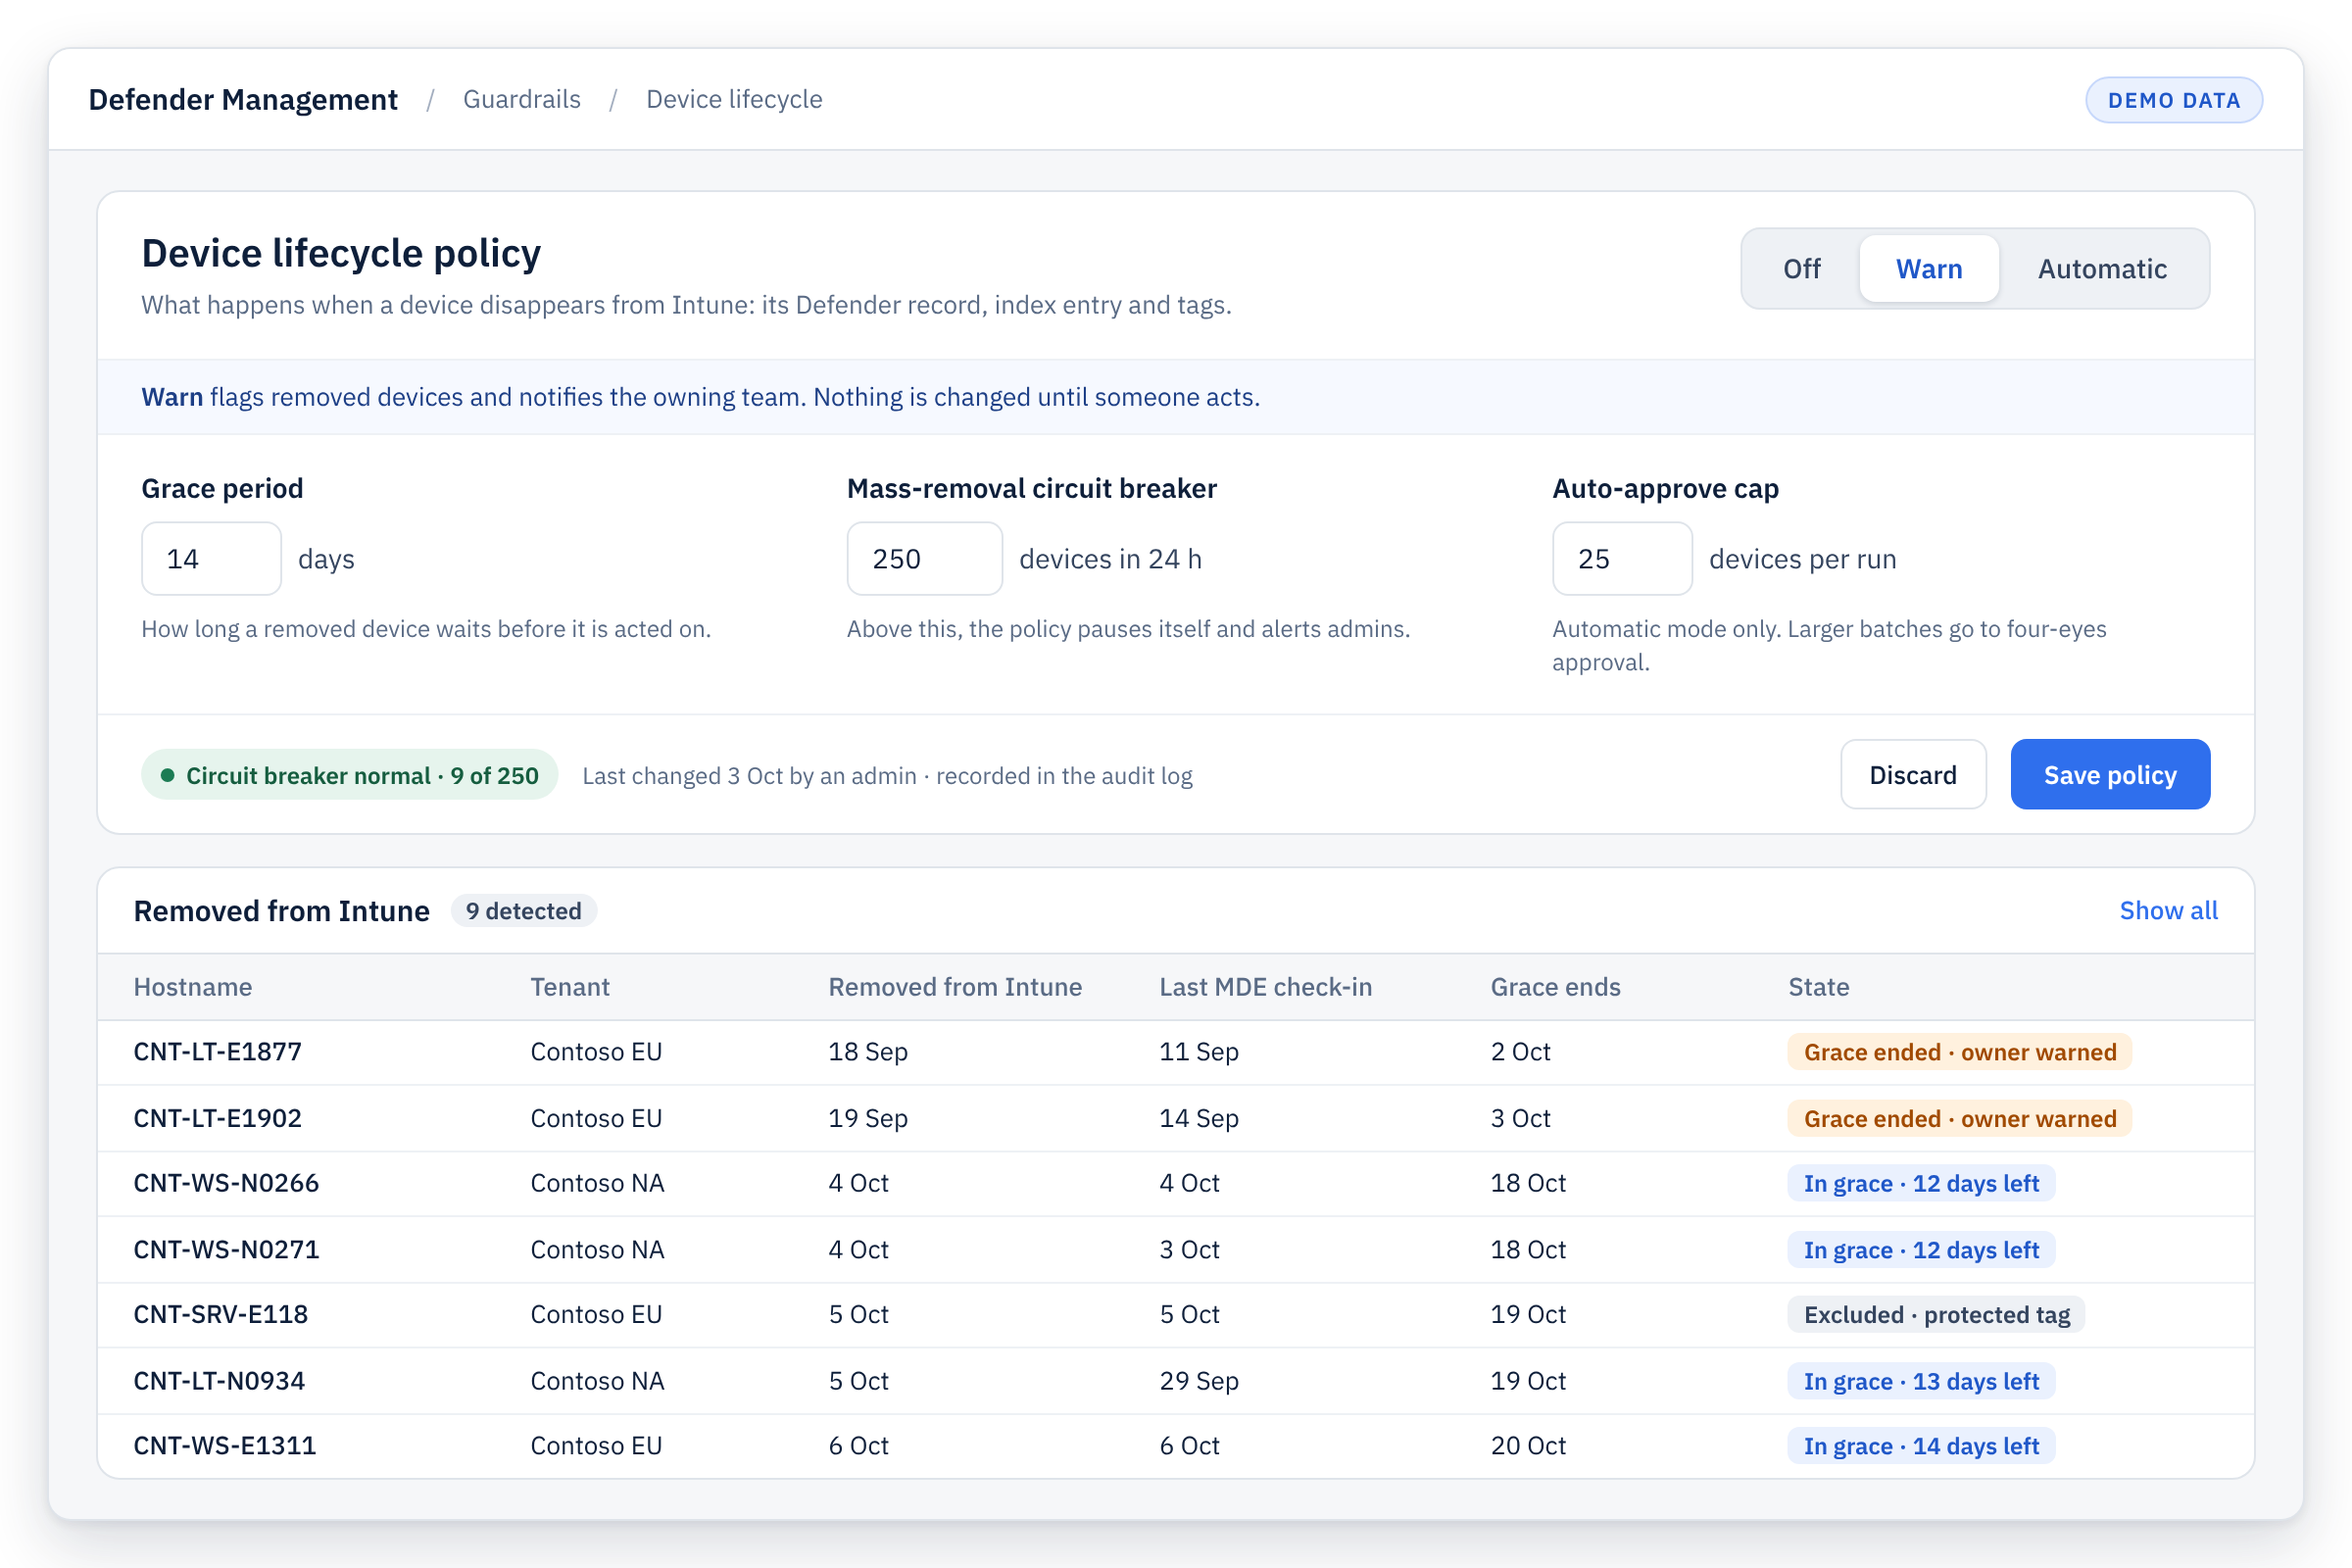
- Protected tags. Crown-jewel and domain-controller assets blocked from disruptive actions.
- Justification required. Sent to Defender as the action comment and kept in the audit log.
- Complete audit trail. Every job, approval, export, hunt and playbook change.
Deployment
Your tenants, your control
- Desktop app. Windows, macOS and Linux, no server required, with per-user and managed (MSI) installers on Windows.
- Shared team server. Container-based deployment for shared approvals, audit and schedules.
- Least privilege. Grant only the application permissions you intend to use.
- Secrets protected. Credentials sealed with the operating-system keychain, and encryption at rest on the server.
- Demo mode. Try a simulated fleet without touching a tenant.
Who it's for
Security engineering teams
Responsible for Defender at scale, and done with one-device-at-a-time work and spreadsheet reconciliation with Intune.
SOC and incident response
Safe, auditable containment and fleet-wide evidence collection without risking critical assets.
Regulated and CNI operators
Provable change control, approvals and an audit trail around endpoint security operations.
See it against your own estate
We work with a small number of organisations at a time. A briefing walks through the product against your tenants, device count and operating model.